GitHub formatter for Sobelow
by Paweł Świątkowski
12 Oct 2026
Two weeks ago a new version of Sobelow was released. Sobelow is a static code analysis tool focused on security and these days it is a de facto standard for providing a minimal security measures to Elixir projects. I am mentioning this release because it contains one feature suggested and developed by me: Github Workflow commands formatter.
The strory behind this feature is relatively simple and may sound familiar. When you have Sobelow check added as a Githb Aciton on your PR and the code change actually violates on of the rules, the check fails and you need to go to the job output to read it. This is bearable, but if you are like me then you probably are not a fan of Github Actions UI in the web and find it at the very least tedious.
The standard alternative is to generate Sobelow report in a SARIF format and upload to the Github Code Security. This has a few upsides, especially for public repositories, but might have drawbacks in enterprise projects – the violations are only visible to admins and you need to have Github Code Security enabled. Also, if I’m not mistaken, this always passes, just reporting the potential security violation, but does not act as a gate check for the pull request.
While investigating the topic for my company, I discovered a third way. After adding it to our CI, I created a pull request to Sobelow and it was merged. It adds additional formatter which uses Github Workflow commands to put the annotations next to the code diff. Since this is one of the cases when image is worth more than 1000 words, here it is:
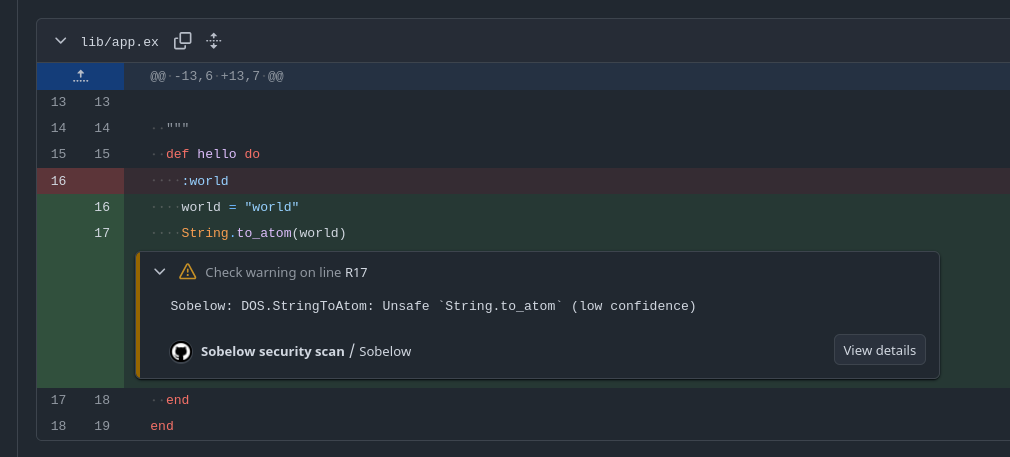
To get this, you simply need to change the formatter in the CI job, like this:
mix sobelow --exit --format github
Hope you will find it useful as we did. This was part of my work as Elixir Open Source contributor at Jump.